01 Distinct connections. One governed layer across the AI estate.Model neutralEdge enforcedOpenAI compatibleAudit ready
The problem
Your AI stack is already plural. Governance shouldn’t be.
Most teams rebuild the same layer from gateway glue, environment variables, request logs, and spreadsheets. Cercloud turns that accidental infrastructure into one deliberate control plane.
Product / Enterprise
Control without constraining the work.
Developers keep the tools and models that make them effective. The organization gets a legible, enforceable system around them.
01 / POLICY
Decide what is allowed—once.
Approved connections, per-task routes, and shared skills become signed policy, not tribal knowledge.
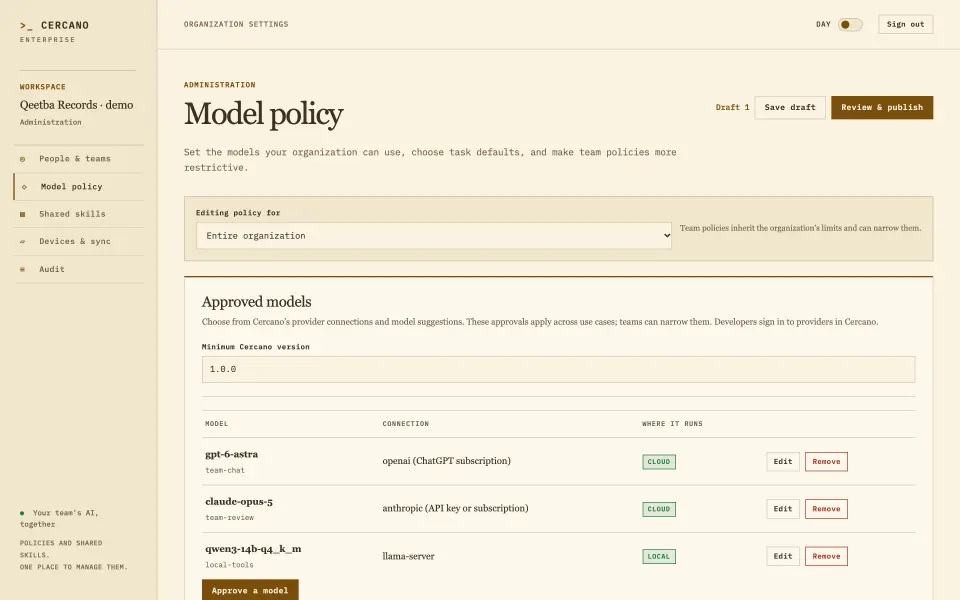
Admins publish immutable revisions. Each enrolled Cercano host fetches a short-lived signed bundle and evaluates it before inference, failing closed when the lease expires.
CONSOLE / POLICY Model access, task defaults, and review before publish.
02 / ROUTING
Use the right model path.
Keep frontier models for the work that needs them. Move routine and sensitive tasks to cheaper or local destinations.
Cercloud governs a mixed estate instead of forcing it into one vendor. Cercano optimizes at the source; the control plane applies policy across the fleet.
Local runtimes
Partner backends
Frontier APIs
Any compatible harness
InterfacesCercanoIDE + agentsCompatible apps
Control planePolicyIdentityRoutingAudit
Local
Partner
Frontier
03 / COST GOVERNANCE
Make every token earn its place.
Drive spend down through better decisions, not a race to mark tokens up less.
Route routine work to efficient models and providers, reserve frontier models for the tasks that need them, and reduce the context each request carries through compaction and caching. Then put budgets, quotas, showback, and chargeback around the whole fleet.
Identity turns policy into permission, usage into attribution, and an audit event into an accountable action.
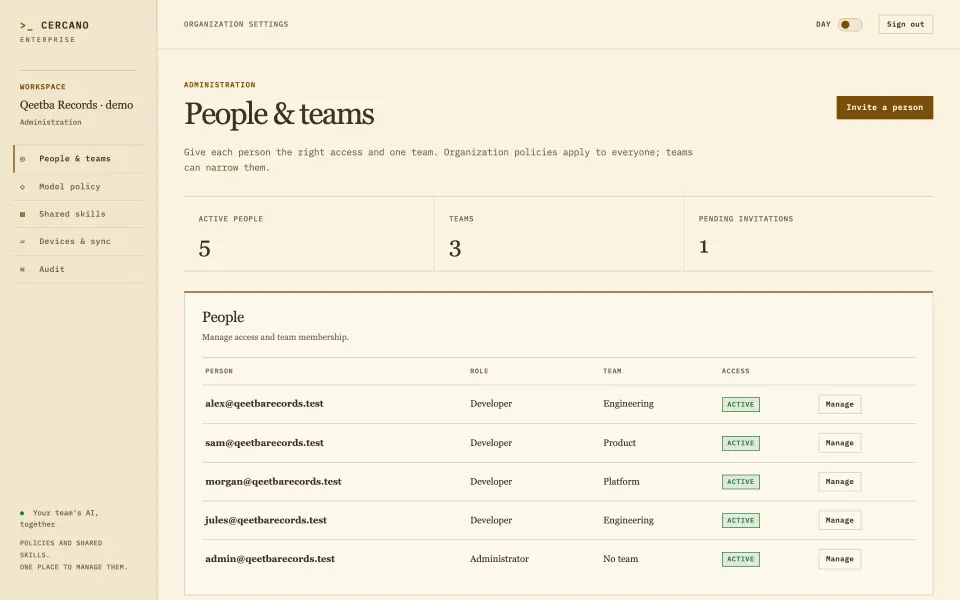
Connect Google Workspace over OIDC or integrate through SAML 2.0, SCIM 2.0, and LDAP. Cercloud binds organization membership, directory groups, roles, and enrolled hosts to permissions—then attributes every governed action to the person behind it.
CONSOLE / IDENTITY People, roles, teams, and access in one organization view.
05 / VISIBILITY
Know who used what—and why.
Tie every governed action to a person, device, team, model connection, task, and policy revision.
Turn usage, latency, and cost into something finance, security, and engineering can act on—without asking developers to reconstruct the story from logs.
AUDIT / 05 Attribution in. Actionable evidence out.
How it works
One policy loop. Every request.
01
Connect the estate
Register approved providers, endpoints, local runtimes, and model connections.
02
Publish policy
Set routes and shared skills by organization, team, task, and connection.
03
Enforce at the edge
Signed policy is verified by Cercano before each inference request runs.
04
Audit the result
Activity returns with identity, device, task, route, and revision attached.
The Trust Layer
Security claims should be inspectable.
One inspectable policy surface connects identity, model access, data handling, deployment boundaries, and the audit trail behind every request.
Identity + access
Google Workspace sign-in
Per-org tenant isolation
Approved model connections
Per-task routing
Signed policy with short leases
Tamper-evident admin audit
Device enrollment and revocation
Data + infrastructure
In-flight PII and PHI redaction
Output filtering and guardrails
Data-residency enforcement
Retention controls
SAML 2.0
SCIM and LDAP
Optional inference proxy
Operated-in-your-boundary deployments
One family / Three tiers
Start open. Add persistence. Govern the organization.
The agent developers choose and the control plane the organization needs, designed as one system.
The managed control plane for the whole AI estate.
Identity and tenant isolation
Policy and model governance
Device and audit visibility
Contract pricing and support
The control plane
Govern the work. Not the developer.
Cercloud gives regulated teams a governed path to local and cloud AI: enterprise identity, enforceable policy, cost controls, and a complete audit trail without another token reseller in the middle.